

Channels, referrers and campaigns
ShieldLabs scores every acquisition channel, referrer and campaign by the Risk Score of the identifications it sends, not by volume alone. Two channels with the same number of identifications are not equal when one runs Trusted and the other runs Dangerous: that gap is the difference between paying for real customers and paying for masked traffic. ShieldLabs assigns every identification to one acquisition channel: from the ad click ID first, then the UTM tags, then the referrer. The channel set is fixed:
A source’s risk is the average Risk Score of the identifications it sent, on the same 0 to 100 scale, read with its band:
Referrers and UTM campaigns
Inside a channel, break traffic quality down by the referring site and by UTM tags. Each identification carries them intraffic_source on the webhook: channel, referrer_domain, landing_url, utm_source, utm_medium, utm_campaign, utm_content, utm_term and click_id_type.
- Referrer: the referring site (for example
news.ycombinator.com). This is how you find the one inbound link, partner site or affiliate sending masked traffic while the channel still looks fine. - UTM tags: source, medium, campaign, term and content, as set on the landing URL.
This is the resolution that drives spend decisions. Google Ads averages 40, Suspicious. By UTM campaign, that is one clean campaign averaged with one at 80, Dangerous, and
utm_content isolates the single creative behind it. You pause what the data shows, ranked by risk.
Dangerous identifications on ad and social channels are flagged too: detection_flags.suspicious_paid_click is true when an identification lands on the Google Ads, Meta, TikTok, LinkedIn, X, Pinterest or Microsoft Ads channel with a Risk Score of 60 or more. The flag carries no weight. The Meta, TikTok, LinkedIn, X and Pinterest channels include organic referrals, so read click_id_type and the UTM tags in traffic_source when you need paid clicks only. Use the flag to isolate Dangerous identifications on these channels without re-deriving channel and Risk Score yourself.
Rank each paid and organic source by the risk of the traffic it sends and the share of risky users it brings, and measure cost per real customer rather than cost per click. A campaign that sends 50,000 clicks at an average of 70, Dangerous, is inflating your click count and your real cost per customer.
How it compares
Pageview analytics counts page loads and cookies. ShieldLabs answers the questions it leaves open:Traffic quality
Traffic quality is the headline reading for a period: one figure on the same 0 to 100 scale as the Risk Score, computed from the period’s identifications. On Overview, the Traffic quality gauge is the average Risk Score of the period’s identifications, with its band word, next to the Identifications count and the Trusted, Suspicious and Dangerous shares.Traffic quality counts identifications, the event layer. Users, devices and unique visitors count identities: one signed-in user who comes back on ten different days is at least ten identifications and one user. Read both: a source with many identifications from few users is a different problem from a source that brings many risky users.
request_id. On the Identifications tab of Analytics you can:
- Filter by band (Trusted, Suspicious, Dangerous) and by High-Risk Events, country, browser, OS, device type, connection type, domain, channel, source, campaign, entry page and risk signals.
- Search by one identifier:
user_hid,device_id,visitor_id,ip,request_id,session_idorcookie_id. - Sort by date and Risk Score.
- Export the identifications behind the current view to CSV. Exports never count against your included identifications. The export holds every identification in the current filter, not only the visible page, up to 10,000 rows.
Reading a risky source
When a channel, referrer or campaign runs Suspicious or Dangerous:- Read the risk signals that push its average up: VPN and proxy traffic, datacenter IPs, anti-detect browsers, browser automation. What each one means is on Risk Signals.
- Look at who the traffic belongs to. Export the source’s identifications, or read them in your backend, and count distinct users and devices. Many identifications from a handful of devices is automated or farmed traffic. Several new accounts on the same devices is what ShieldLabs detects as Multi-accounting; High-Risk Events are available in the analytics dashboard, the API and webhooks.
- Act per source and per account. Pause the placement, hold the affiliate’s payout, and step up or review the accounts the source brought. You choose the action for each case.
Traffic quality in your backend
Each webhook carries the identification’s source intraffic_source, next to its user_hid, device_id and risk_score. Aggregate on the identities to score campaigns by the users they bring, not by clicks:
Risky users per campaign (Node.js)
In the analytics dashboard
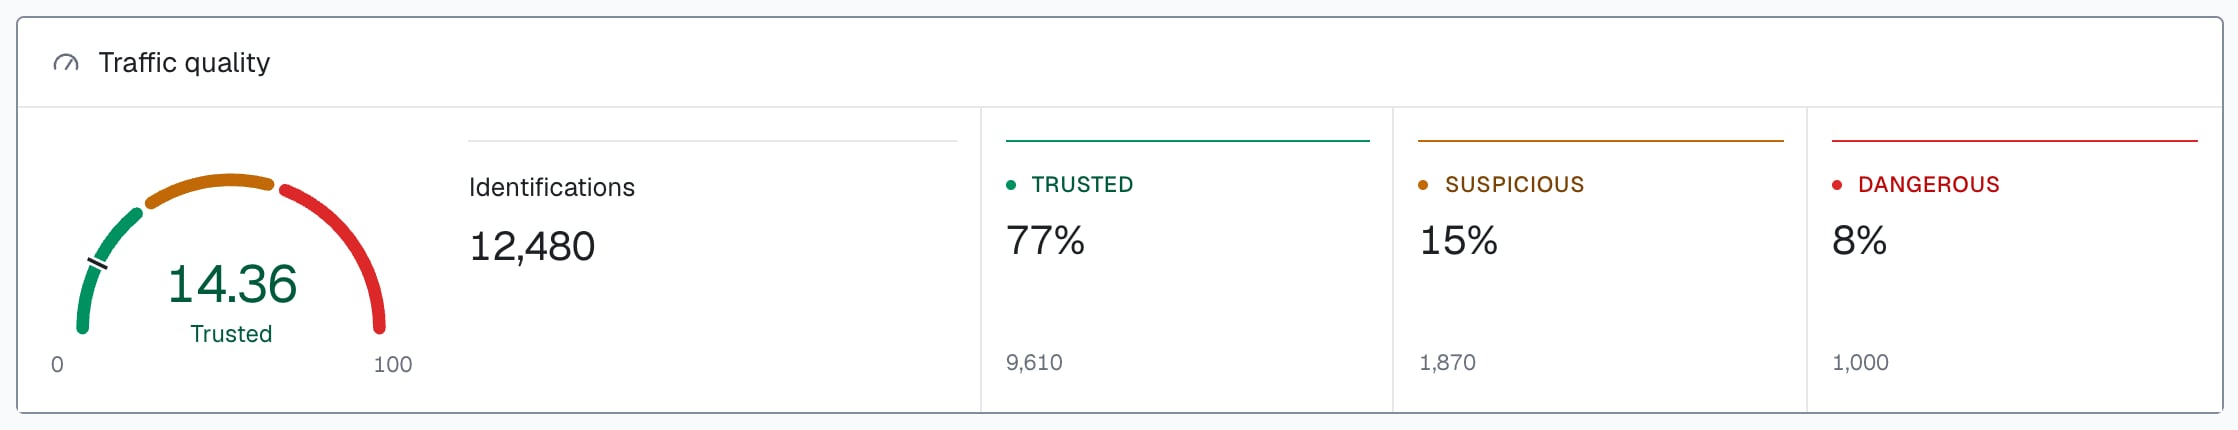
Traffic quality in the analytics dashboard: the average Risk Score of the period's identifications and their split across Trusted, Suspicious and Dangerous.
- Overview opens with Traffic quality. The Top channels list shows the identifications and the average Risk Score of each channel. The other top lists cover countries, browsers, OS, connection types and device types. The Unique visitors panel counts good bots (search-engine crawlers) and bad bots (browser automation) among your visitors.
- Click a channel to open Analytics filtered to it. Switch to the Users tab to see the users whose own identifications carry that channel, each with its worst band; open a user to see its High-Risk Events. The Unique visitors, Devices and Public IPs tabs work the same way. Add Source, Campaign or Entry page filters to narrow it to one campaign.
- Open a user to see its linked devices, visitors and IP addresses, and the identifications behind its band (User, device, visitor and IP cards).
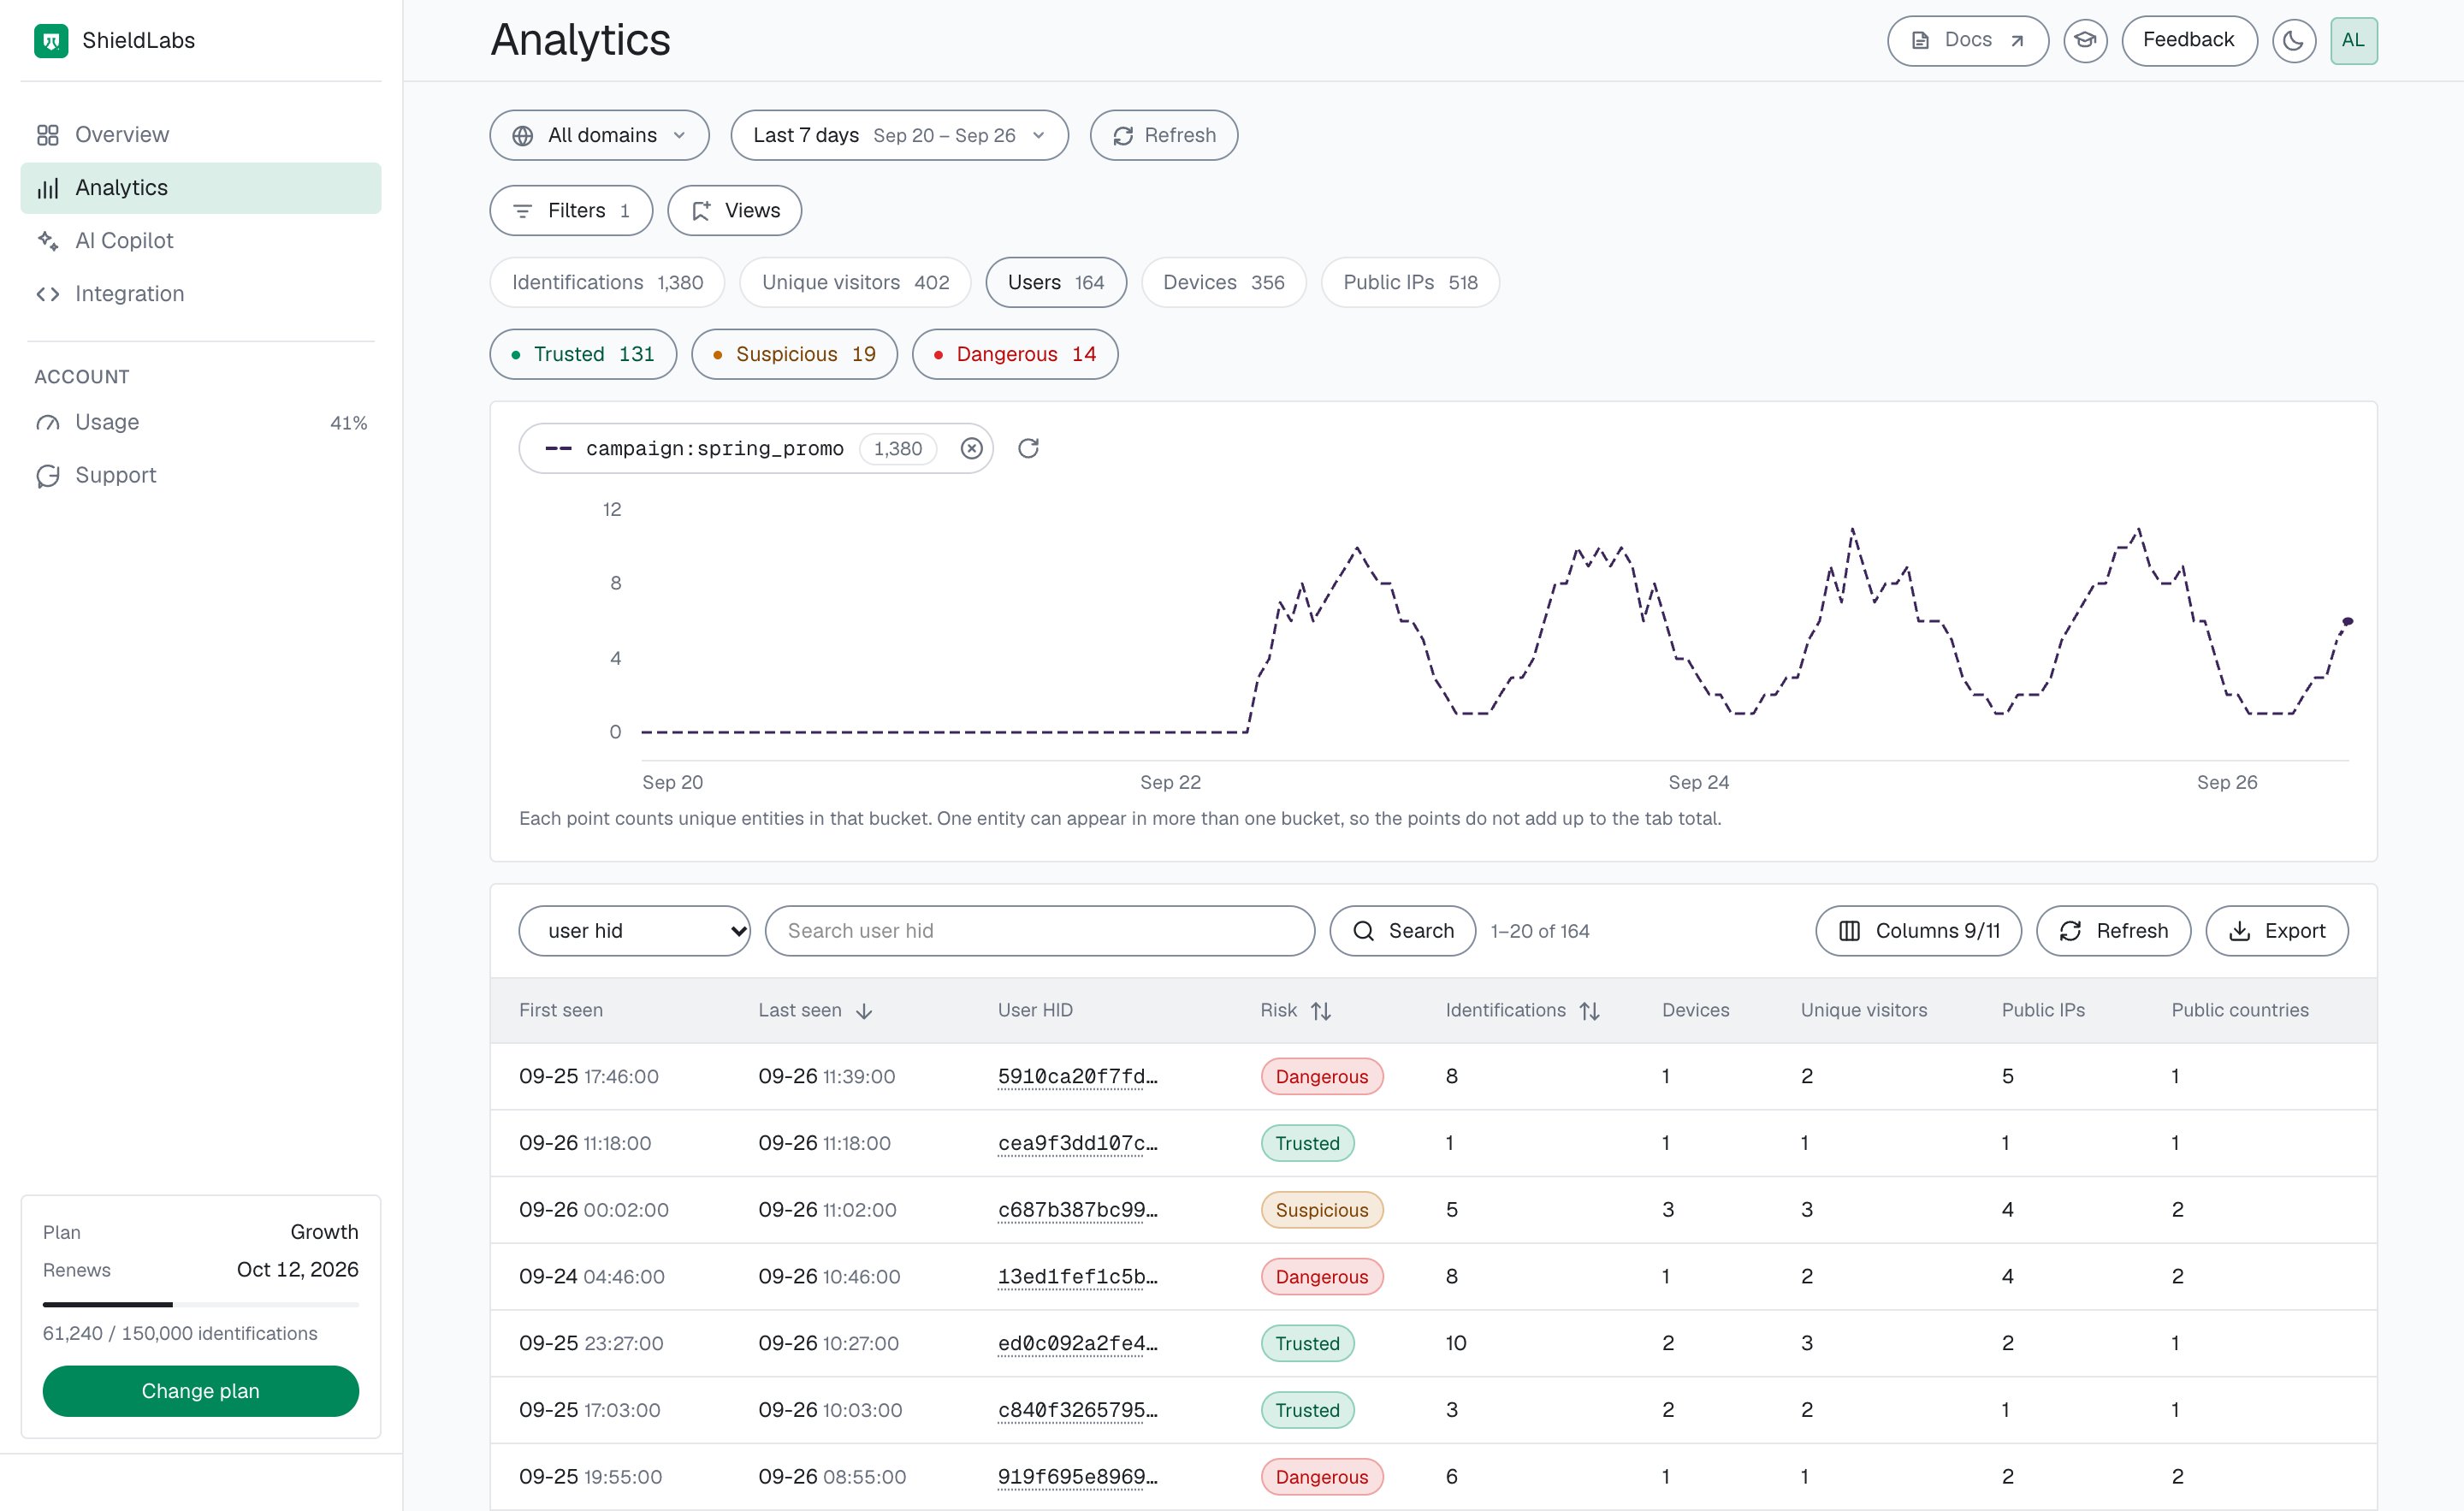
The users whose identifications carry one campaign, each with its band, in the analytics dashboard.
Next steps
Risk Signals
Every risk signal behind a source’s risk, from VPN and Tor to anti-detect browsers and browser automation, with its weight.
Traffic quality
Measure traffic quality per source over time and track cost per real customer in your backend.
Affiliate fraud
Score traffic per affiliate and per campaign, find the partner sending masked clicks, and reconcile payouts against the real customers each partner brings.